Pick a narrow first scenario
Good starting points are guiding visitors through your services, explaining how to prepare for a consultation or collecting the initial details of a request. Take a set of real, anonymized questions and check whether you have approved answers for them. If your sources contradict each other, sort them out first.
Don't start by promising it will "answer everything." The broader the task, the harder it is to verify the result. It's better to define one specific, useful path and expand it after testing.
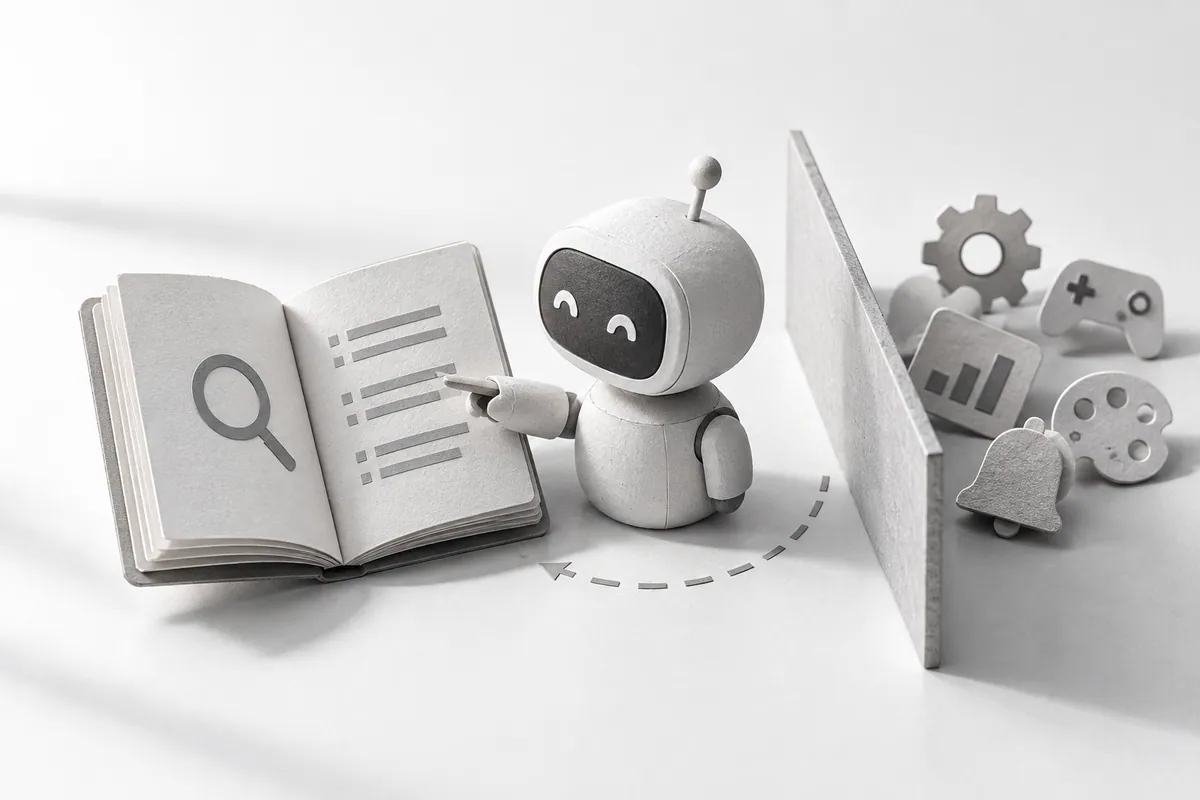
Answering and acting need different permissions
Explaining how you work and changing an order require different levels of access. Operations on data need identity checks, limited permissions and confirmation of important actions. A user's message must never automatically become permission to run arbitrary commands.
OWASP describes the risks of LLM applications, including prompt injection and excessive agency. The practical takeaway for a business: limit integrations to the task at hand and test how the bot behaves on unusual requests. For more on automation with proper error handling, see n8n for business.
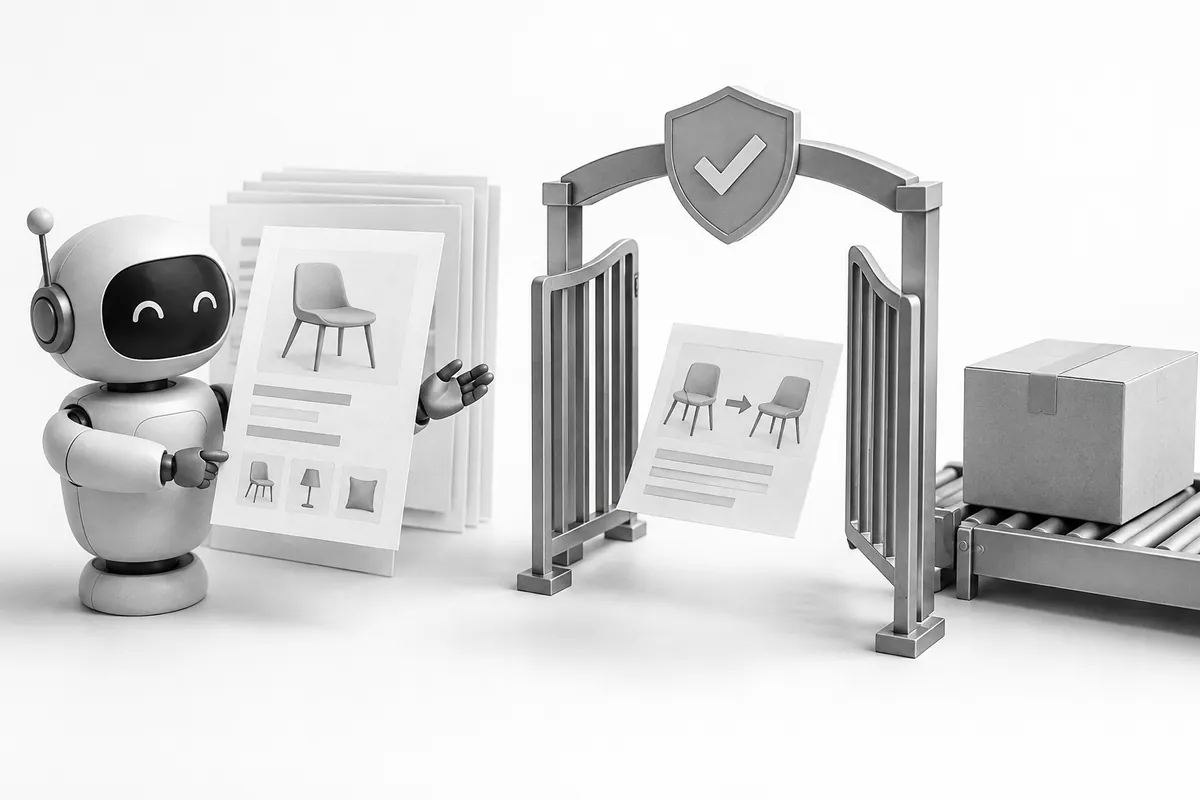
A handoff to a person must keep the context
The bot should say honestly when it doesn't know the answer or when a question goes beyond its scenario. Pass the specialist a short summary, the contact details the customer agreed to share and the information already collected. The customer shouldn't have to repeat the whole conversation. How these requests are routed is covered on the lead generation page.
When building an AI chatbot, agree on a set of tests, including refusals and handoffs. CRM integration helps keep every request on record, but it doesn't replace the person responsible for following up.